Skip to content
VerifiX, secured by ITSEC

Platform · Travel Rule

Travel Rule, handled before the transfer leaves.

Counterparty VASP discovery, originator and beneficiary data exchange, unhosted-wallet ownership proof, and a message record for every qualifying transfer, evaluated in the same call that screens the wallet.

Inside the handshake

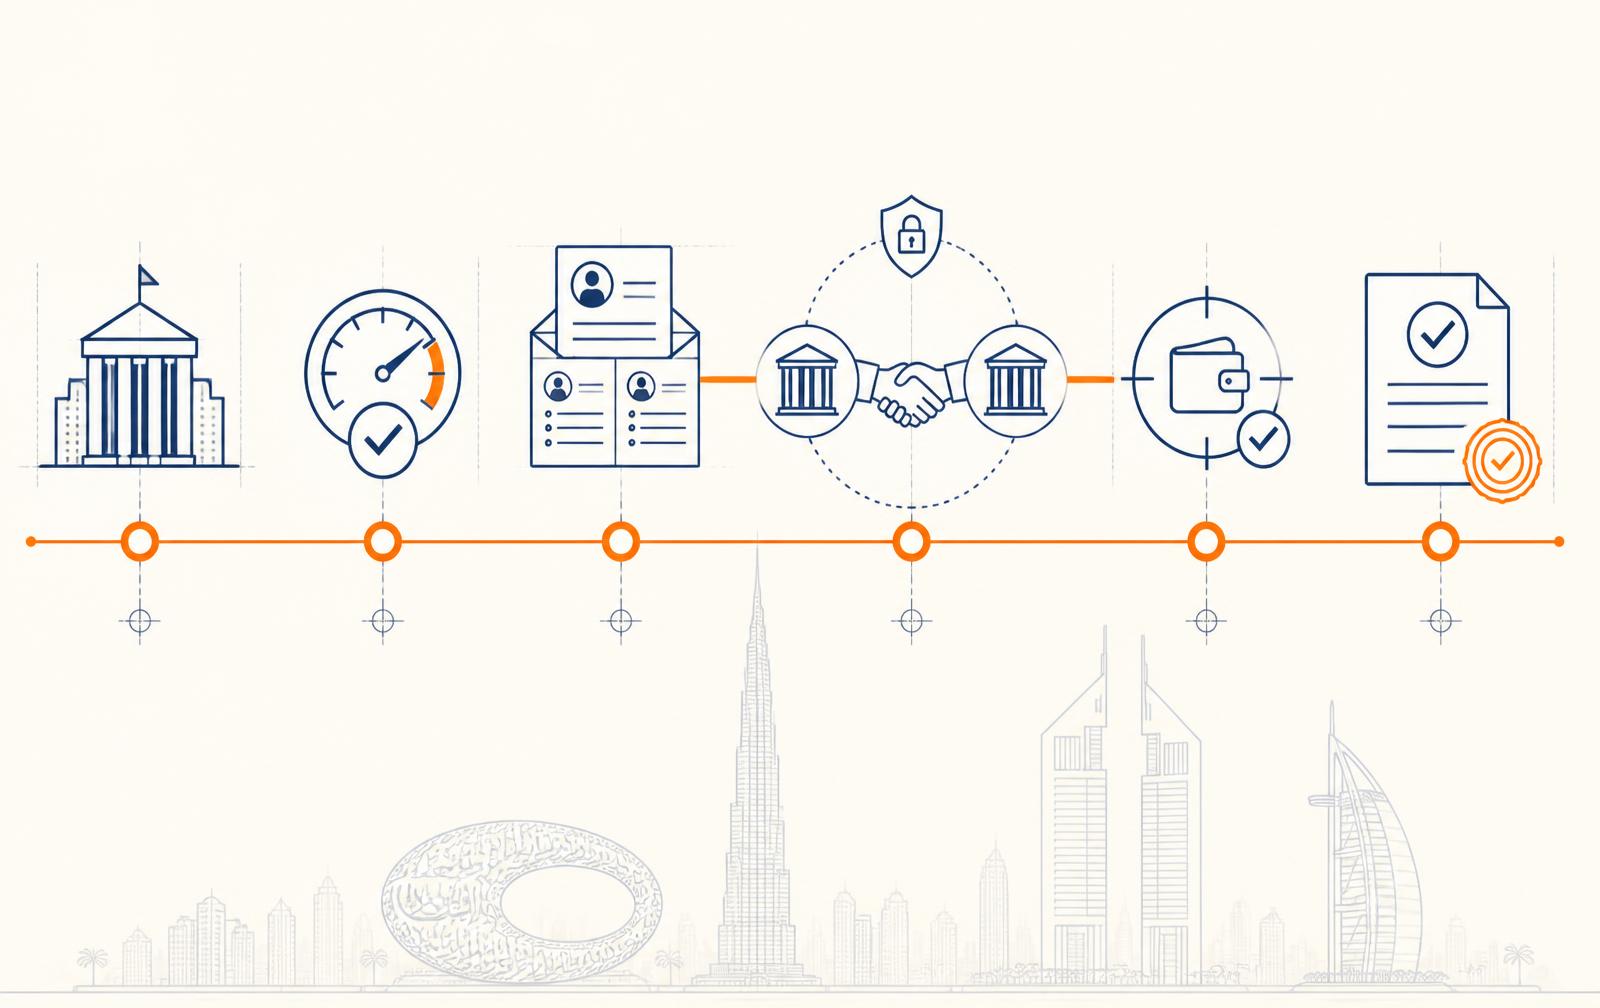
What happens before the transfer leaves

Threshold test, counterparty resolution, payload exchange, and the sunrise-case fallback when the other side cannot receive.

01

Scope determination

Every transfer is tested against the applicable threshold and transfer type before any data leaves your tenant, the AED 3,500 threshold.

02

Counterparty VASP discovery

The destination address is attributed to an institution where attribution exists, and matched to a reachable counterparty, counterparties are reached over Notabene and TRP.

03

Originator and beneficiary data

Required originator and beneficiary fields are assembled from the verified customer record rather than re-typed, so the message matches the KYC evidence on file.

04

Unhosted wallet handling

Self-custody destinations trigger ownership proof, declaration, signed message, or in-session verification, self-hosted wallets are evidenced with signed-message or micro-transfer proof.

05

Sunrise and refusal handling

When a counterparty cannot receive a message or refuses to respond, the transfer is routed to a documented decision, proceed, hold, or reject, with the reason recorded.

06

Inbound message review

Incoming originator data is validated against the beneficiary you hold, and mismatches open a case instead of silently crediting the account.

07

Screening in the same call

Sanctions screening of the counterparty parties and wallet exposure scoring run alongside the message, so one decision covers both obligations.

08

Message record

What was sent, what came back, when, and under which protocol version, retained on the customer's case file.

Submission to settlement

How a transfer clears the rule

The originating side and the beneficiary side of the same exchange, in order.

  1. 1

    Submit the transfer

    Send the transfer against a customer ID that already carries verified identity data, before you broadcast or release funds.

  2. 2

    Determine scope and counterparty

    VerifiX decides whether the transfer is in scope, attributes the destination, and resolves whether it is an institution or an unhosted wallet.

  3. 3

    Exchange or prove

    Originator and beneficiary data is exchanged with the counterparty institution, or ownership proof is collected for a self-custody destination.

  4. 4

    Decide and release

    Hold, proceed, or reject based on the response, the screening result, and your own rules, with the outcome attached to the case.

  5. 5

    Retain the evidence

    The message, the response, the proof, and the decision are written to the append-only audit trail with the operator who approved it.

Transaction trace · 0x9f…c204Sample data
  1. 1Customer walletVerified · low
  2. 2Exchange depositLicensed VASP
  3. 3Intermediary2 hops · medium
  4. 4Mixer-linked clusterHigh risk

Exposure

Indirect

Hops

3

Action

Alert raised

POST /v1/travel-rule/transfers
curl -X POST https://api.verifix.ae/v1/travel-rule/transfers \
  -H "Authorization: Bearer $VERIFIX_KEY" \
  -d '{
    "direction": "outbound",
    "asset": "USDT",
    "amount": "12500.00",
    "originator": { "customer_id": "cus_2LX..." },
    "beneficiary": { "name": "A. Rahimi", "wallet": "0x9f2...c41" },
    "jurisdiction": "AE"
  }'

{
  "id": "tr_7QF...",
  "in_scope": true,
  "counterparty": {
    "type": "vasp",
    "resolved": "exchange_partner_id",
    "protocol": "supported_protocol",
    "status": "message_sent"
  },
  "beneficiary_response": "pending",
  "hold": true,
  "evidence_id": "ev_31A..."
}

Chain of custody

One transfer, as the record shows it

Illustrative sample data for an outbound transfer at or above the AED 3,500 threshold.

  1. 13:07:22Transfer submitted · AED 42,000 equivalent
  2. 13:07:22In scope · at or above AED 3,500 threshold
  3. 13:07:23Counterparty resolved · licensed VASP, protocol reachable
  4. 13:07:24Originator and beneficiary payload sent
  5. 13:07:26Counterparty acknowledged · data accepted
  6. 13:07:26Message record sealed · transfer released

Named modules

The Travel Rule modules

Wallet and transaction monitoring modules live on the KYT page.

Travel Rule messaging

4 modules

Scope the transfer, resolve the counterparty, exchange the payload, and record what was sent, received, or refused.

Travel Rule messaging

travel_rule

Exchanges originator and beneficiary information with counterparty institutions on qualifying transfers, and records what was sent, received, or refused.

Input
Transfer details and counterparty VASP
Returns
message record, counterparty response, unhosted-wallet declaration where applicable

Counterparty VASP discovery

counterparty_vasp_discovery

Attributes a destination address to an institution and resolves whether a Travel Rule message can be delivered to it, or whether the destination is an unhosted wallet.

Input
Destination address and chain
Returns
counterparty type, resolved institution, reachable protocol, sunrise flag

Travel Rule scope test

travel_rule_scope

Decides whether a transfer is in scope before any personal data leaves your tenant, using the threshold and transfer rules of the applicable regime.

Input
Transfer amount, asset, direction, jurisdiction
Returns
in_scope flag with the threshold and rule version applied

Unhosted wallet ownership proof

unhosted_wallet_proof

Collects proof that a self-custody destination belongs to your customer: signed message, declaration, or in-session verification, retained as an artefact.

Input
Address, customer ID, chosen proof method
Returns
proof artefact, method used, verification result

See the full module catalog , every KYC, KYB, AML, KYT, and platform module with its inputs and outputs.

Inside the console

A transfer record, not just a message

Counterparty discovery, data exchange, and wallet evidence stay connected to the transfer’s case file.

StageWhat your team sees
ResolveIdentify the counterparty Virtual Asset Service Provider (VASP) before exchanging the payload.
ExchangeSend originator and beneficiary information through Notabene or TRP.
CheckCollect proof of control for an unhosted wallet where the journey requires it.
RetainRecord what was sent, the reply, timestamps, and the protocol version on the case file.

Evidence retained

What proves the payload was exchanged

  • Scope test applied, with the threshold and rule version used
  • Counterparty attribution, institution resolved, and protocol version
  • Exact originator and beneficiary fields transmitted, with timestamp
  • Counterparty response, refusal, or non-response window
  • Unhosted-wallet ownership proof artefact where collected
  • Screening results for both parties at the time of transfer
  • Final decision, operator identity, and reason code
Scope
in_scope · out_of_scope with reason
Counterparty
vasp · unhosted · unattributed
Decision
proceed · hold · reject
Delivery
API response + webhook on counterparty reply
Retention
Set to the period your license requires

Questions

Frequently asked

Which messaging protocols do you support?
Notabene and TRP, which reach the counterparties those networks cover.
What threshold applies in the UAE?
The AED 3,500 threshold applies in the UAE.
What happens with self-custody wallets?
The transfer is flagged as unhosted and an ownership-proof step is required before release. Which proof methods you accept is configurable per journey.
Do we still need separate wallet screening?
No, Travel Rule messaging and wallet exposure scoring share one call and one case record. See screening and Travel Rule messaging run in the same transfer flow.

See VerifiX on your own onboarding flow

A 30-minute walkthrough with a compliance engineer, or a request for sandbox access.