Skip to content
VerifiX, secured by ITSEC

Platform · Case management

One queue, one record, one audit trail.

Alert queues, four-eyes review, escalation paths, SLA timers, and an immutable trail of who decided what, on which evidence, under which rule version.

Inside the queue

What a reviewer actually sees

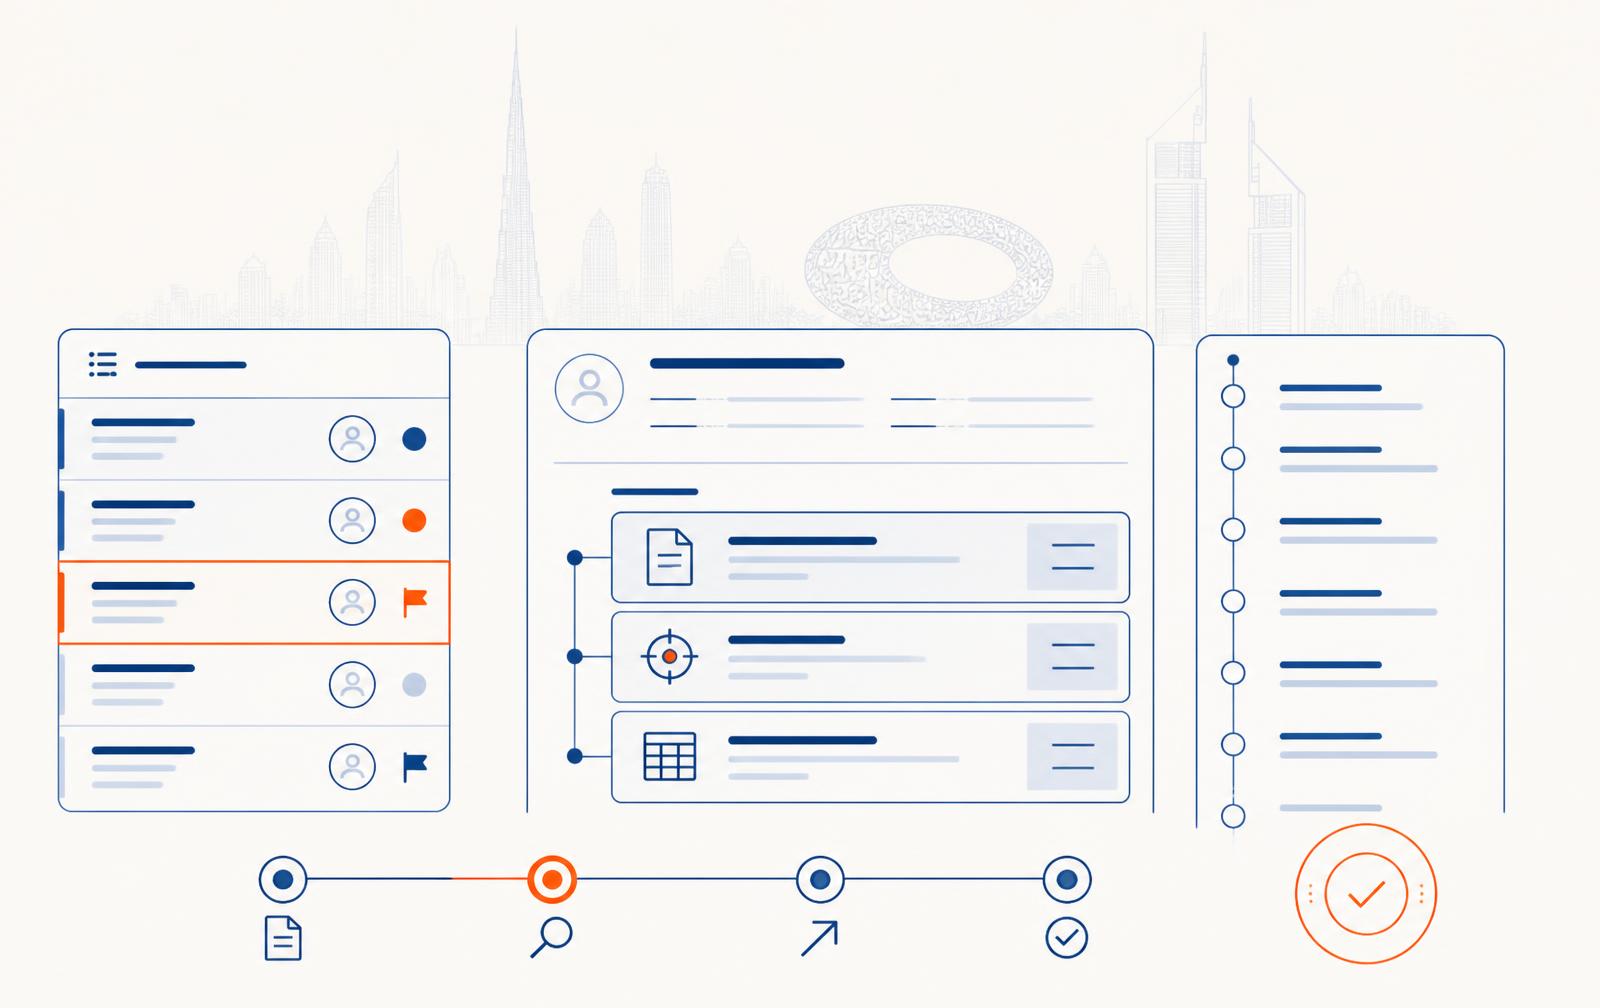
One prioritized queue for every alert type, with the signals that fired, the owner, and the clock already attached.

01

Unified queue

KYC, KYB, screening, and transaction alerts in a single prioritised queue instead of four vendor dashboards and an inbox.

02

Four-eyes review

Maker-checker enforced by role, with configurable thresholds for which decisions require a second approver.

03

Escalation paths

Route to EDD, compliance officer, or MLRO based on risk band, customer type, or triggered rule.

04

SLA timers

Age and breach tracking per queue and per analyst, with reporting for your internal targets, the turnaround your license requires.

05

Immutable audit trail

Append-only history of every view, note, decision, and configuration change, exportable for inspection.

06

Role-based access

Granular permissions separating analysts, reviewers, administrators, and read-only auditors.

Alert to closure

How a case is worked

Assignment, review, four-eyes approval, closure, each step written to the same trail.

  1. 1

    Alert created

    Any non-cleared decision opens a case with the evidence, score breakdown, and customer history already attached.

  2. 2

    Assigned and worked

    Cases are assigned by rule or claimed from the queue; notes and requested documents stay on the record.

  3. 3

    Reviewed

    The decision goes to a second pair of eyes where policy requires it, with the reviewer unable to approve their own work.

  4. 4

    Closed and reportable

    Outcome, reason code, and full trail are retained and exportable for audit or regulatory request.

Audit trail · case VX-40219Sample data
  1. 09:14:02Verification created · journey uae_vasp_retailAPI
  2. 09:14:09Document authenticated, face matchedSystem
  3. 09:14:11Screening run · 1 potential matchSystem
  4. 10:02:47Reviewed match, requested source of fundsAnalyst · S.K.
  5. 14:31:20Approved with EDD note attachedAnalyst · S.K.

Entries are append-only and exportable as evidence

Chain of custody

One case, from open to sealed

Illustrative sample data. Reviewers cannot approve their own escalations.

  1. 09:15:30Case opened · referred from KYC journey
  2. 09:22:11Assigned · analyst M. Obaid, SLA 4h
  3. 10:04:57Note and document added · source of funds
  4. 10:31:02Recommendation submitted · approve with EDD
  5. 11:08:40Second approver signed off · four-eyes satisfied
  6. 11:08:40Case closed · evidence bundle sealed

Named modules

The case and evidence modules

Journey building and risk rules live on the risk engine page.

Case work and evidence

4 modules

The queue your analysts work in, and the record it leaves behind for internal audit and the regulator.

Case management

case_management

Alert queues, assignment, four-eyes approval, escalation paths, notes, and a full decision history for every customer and every alert.

Input
Cases created by journeys and monitoring
Returns
case state machine, reviewer actions, SLA timers

Regulatory reporting workpapers

reporting

Assembles the case narrative, evidence, and decision history into the workpaper an analyst files with the relevant financial intelligence unit.

Input
Escalated case
Returns
report pack, filing record, retained submission evidence

Immutable audit trail

audit_trail

Append-only record of every check, decision, override, policy change, and export, who, what, when, and under which policy version.

Input
All platform activity
Returns
queryable event log and a signed evidence export

Evidence export

evidence_export

Produces a decision PDF or evidence bundle per case, and bulk exports to your warehouse or object storage for inspection and retention.

Input
Case or date range
Returns
PDF, JSON, or archive with a manifest and checksums

See the full module catalog , every KYC, KYB, AML, KYT, and platform module with its inputs and outputs.

Evidence retained

What the trail records about your team

  • Case timeline with every state change and actor
  • All evidence artefacts as they existed at decision time
  • Rule and threshold versions applied
  • Notes, document requests, and customer communications
  • Export bundle per case or per date range
Case states
open · in review · escalated · closed
Reason codes
configurable per outcome, mandatory on close
Retention
Set to the period your license requires
Export
per-case bundle and bulk audit export

Questions

Frequently asked

Can auditors get read-only access?
Yes, a dedicated auditor role can read cases and export trails without the ability to alter any record.
Does the trail cover configuration changes?
Yes. Rule edits, threshold changes, and permission changes are versioned alongside case activity.
Can we integrate our existing ticketing tool?
Cases sync out over webhooks and API to your ticketing or CRM system.

See VerifiX on your own onboarding flow

A 30-minute walkthrough with a compliance engineer, or a request for sandbox access.